Find vulnerabilities before attackers do.
We simulate real-world attacks against your systems, applications, and people to expose weaknesses, prove risk, and deliver clear, prioritized fixes — not just a list of problems.
Ready to reduce risk?
Protect your systems before attackers find you.
Contact us to request a quote or schedule a free scoping call — we’ll map the right test to your business goals and compliance needs.
What we test
External network / perimeter — servers, firewalls, VPNs that are reachable from the internet.
Internal network — lateral movement, misconfigurations, weak credentials inside your LAN.
Web applications & APIs — OWASP Top 10, business-logic faults, session/auth issues.
Mobile apps (iOS / Android) — local storage, insecure communications, client-side logic.
Cloud environments — AWS / Azure / GCP misconfigurations, IAM issues, exposed storage.
Wireless and IoT — insecure devices, weak encryption, rogue access points.
Social engineering (phishing / phone) — real-world user-target tests (conducted with consent).
Red team exercises — long-form, goal-based adversary simulation combining technical and human attack vectors.
Our approach
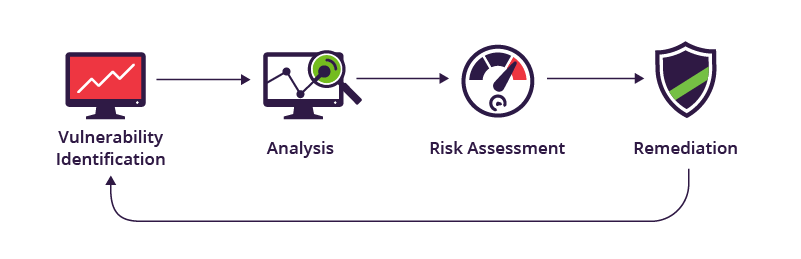
Scoping & Rules-of-Engagement — agree objectives, targets, time window, and safe-guards.
Reconnaissance — passive and active discovery to map attack surface.
Vulnerability identification — automated scans + manual review to find weaknesses.
Exploitation & validation — safely prove impact where permitted (no destructive actions).
Post-exploitation & risk analysis — determine business impact and lateral risks.
Reporting & remediation guidance — clear executive summary, technical details, and prioritized fixes.
Retest & verification — confirm fixes and validate improved security posture.
Deliverables you’ll actually use
Executive summary
Non-technical overview for leadership and risk owners.
Technical findings
Reproducible steps, evidence, affected components, and CVSS where applicable.
Priority remediation roadmap
Quick wins, medium-term fixes, long-term security projects.
Risk scoring & business impact
Helps prioritize fixes by likelihood and damage.
Retest report
Verification of remediated issues.
Optional: compliance mapping
Alignment to ISO 27001, PCI-DSS, NIST, GDPR (where needed).
Frequently Asked Questions
Our FAQ section helps you understand what penetration testing is, how it works, and what to expect from our service. Whether you’re new to cybersecurity or already managing complex systems, these answers will guide you through the testing process, timelines, and benefits — ensuring full transparency before we begin.
We design tests to minimize disruption. Exploitation is performed safely and only with prior agreement. Critical systems can be excluded or tested in a staged environment.
You’ll receive a draft technical report and executive summary typically within 5–10 business days after testing completes. ( Exact timing depends on scope. )
Yes — we provide remediation guidance and can work with your engineers or offer follow-up retests to verify fixes.
Our team holds practical security certifications and extensive real-world experience. Certification details available on request.
All engagements are covered by NDA and secure evidence handling procedures. We keep data encrypted and limit access to the project team.